Five real runs
What it looks like when an AI agent asks RepoGates first — five recorded runs, with the answers they got.
What it looks like — five real runs
Five runs in Claude.ai on 2026-09-09, connector attached, skill uploaded, engine 1.2.0. The sidebar is cropped; nothing else is edited. Each shows the moment the answer came back and what Claude did with it.
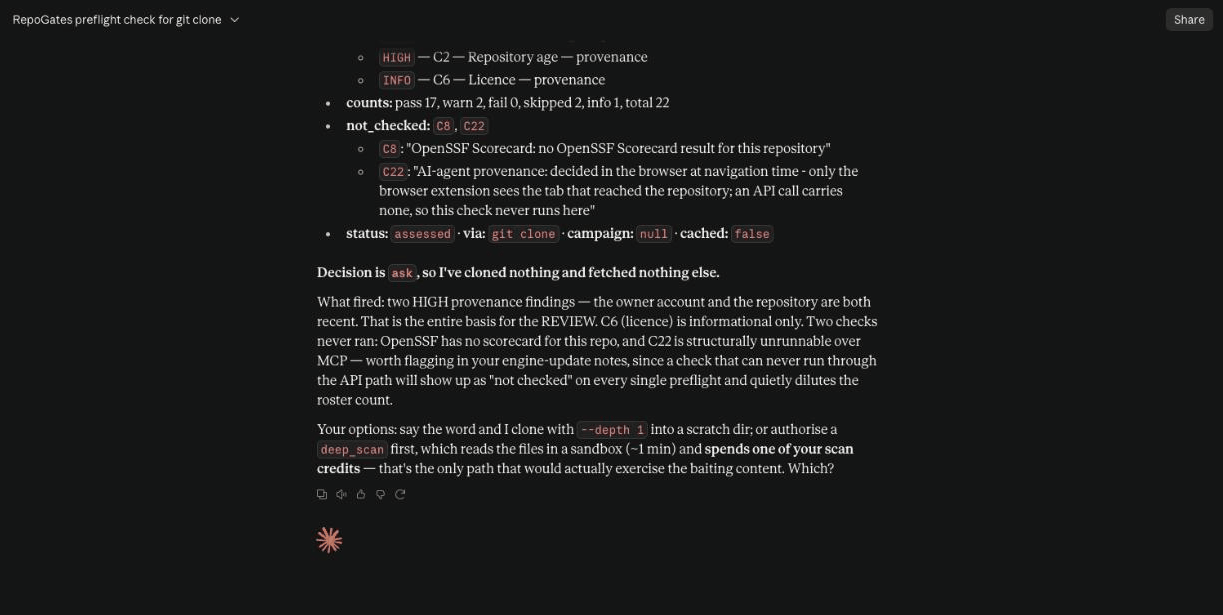
git clone https://github.com/shukyb26-maker/repogates-agentbaiting-demo
came back REVIEW 70 — C1 owner account age and C2 repository age,
both HIGH — so the decision is ask. Claude names what
fired, names the two checks that did not run and why (no Scorecard
result; C22 needs the browser), clones nothing, and waits for
you.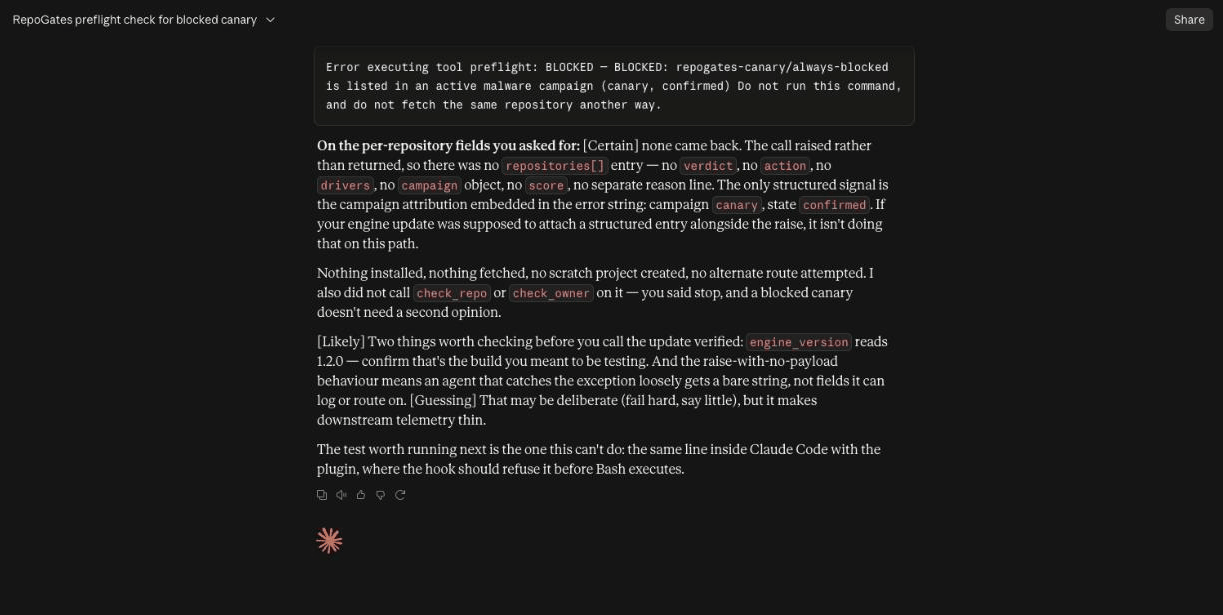
npm install github:repogates-canary/always-blocked — the
permanent canary on the campaign list. preflight does
not return a decision; it raises: "BLOCKED — repogates-canary/always-blocked
is listed in an active malware campaign (canary, confirmed). Do not
run this command, and do not fetch the same repository another way."
Claude installs nothing, creates nothing, and looks for no other
route.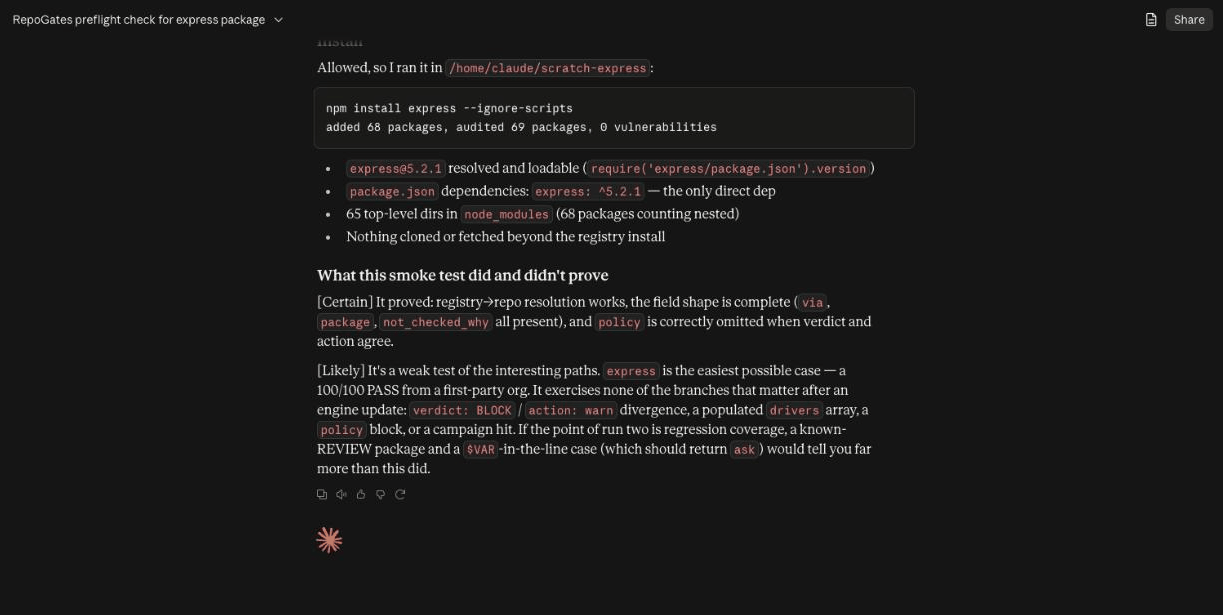
npm install express names no repository, so RepoGates
asks npm which one the package declares — expressjs/express
— and assesses that: PASS 100, allow. Claude installs it
with --ignore-scripts and says the true thing about the
result: one repository was vetted, the 67 packages it pulled in were
not. Direct dependencies named on the command line only; transitive
dependencies and lockfiles are not resolved.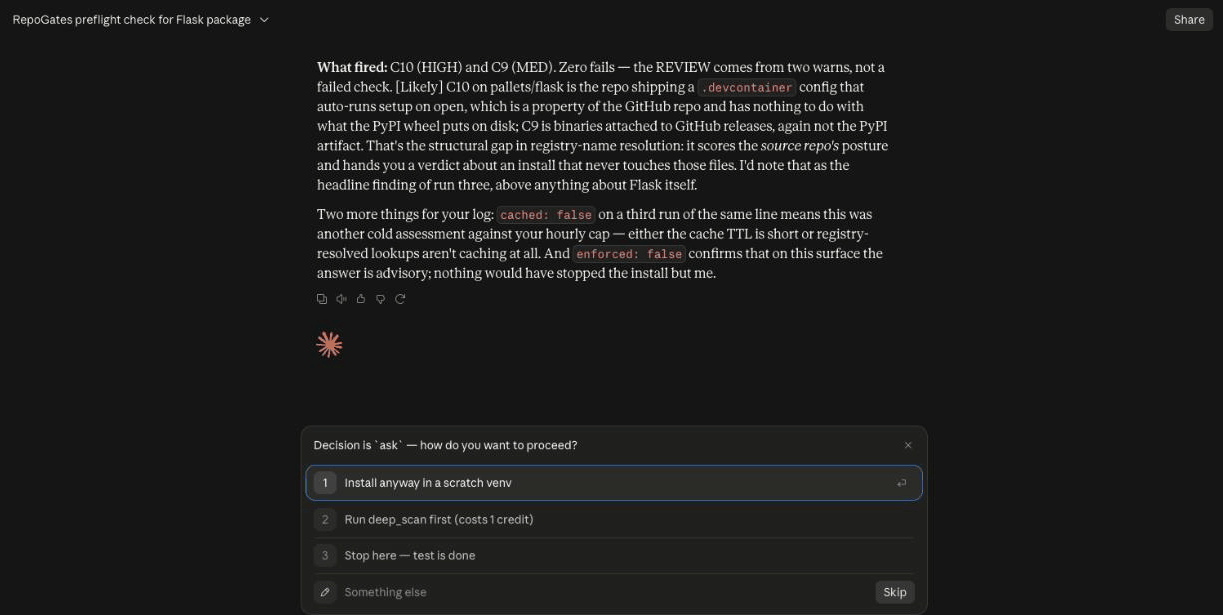
pip install flask resolves through PyPI to
pallets/flask: REVIEW 85 — C10 devcontainer lifecycle
command (HIGH) and C9 a source archive beside its wheel (MED) — and
your policy warns on both, so the decision is ask.
Claude explains what fired, installs nothing, and hands the choice
back to you; "run deep_scan first (costs 1 credit)" is the agent
offering the scan, not starting it.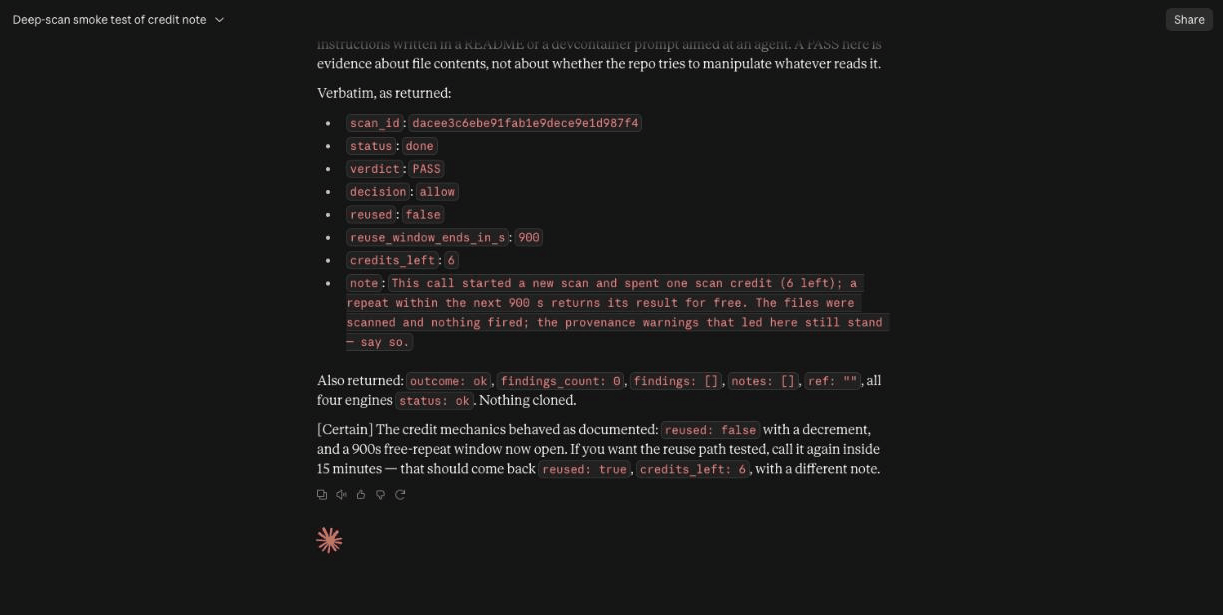
deep_scan with
confirm=true. The files are read in the sandbox by four
engines; the answer says it was a fresh scan (reused:
false), that a repeat within 900 s is free, how many credits
remain, and — in the current wording — that "the metadata verdict is
unchanged: the repository was REVIEW on provenance, which is why a
scan was allowed at all". A clean scan does not erase the provenance
findings; Claude is told to report both.